
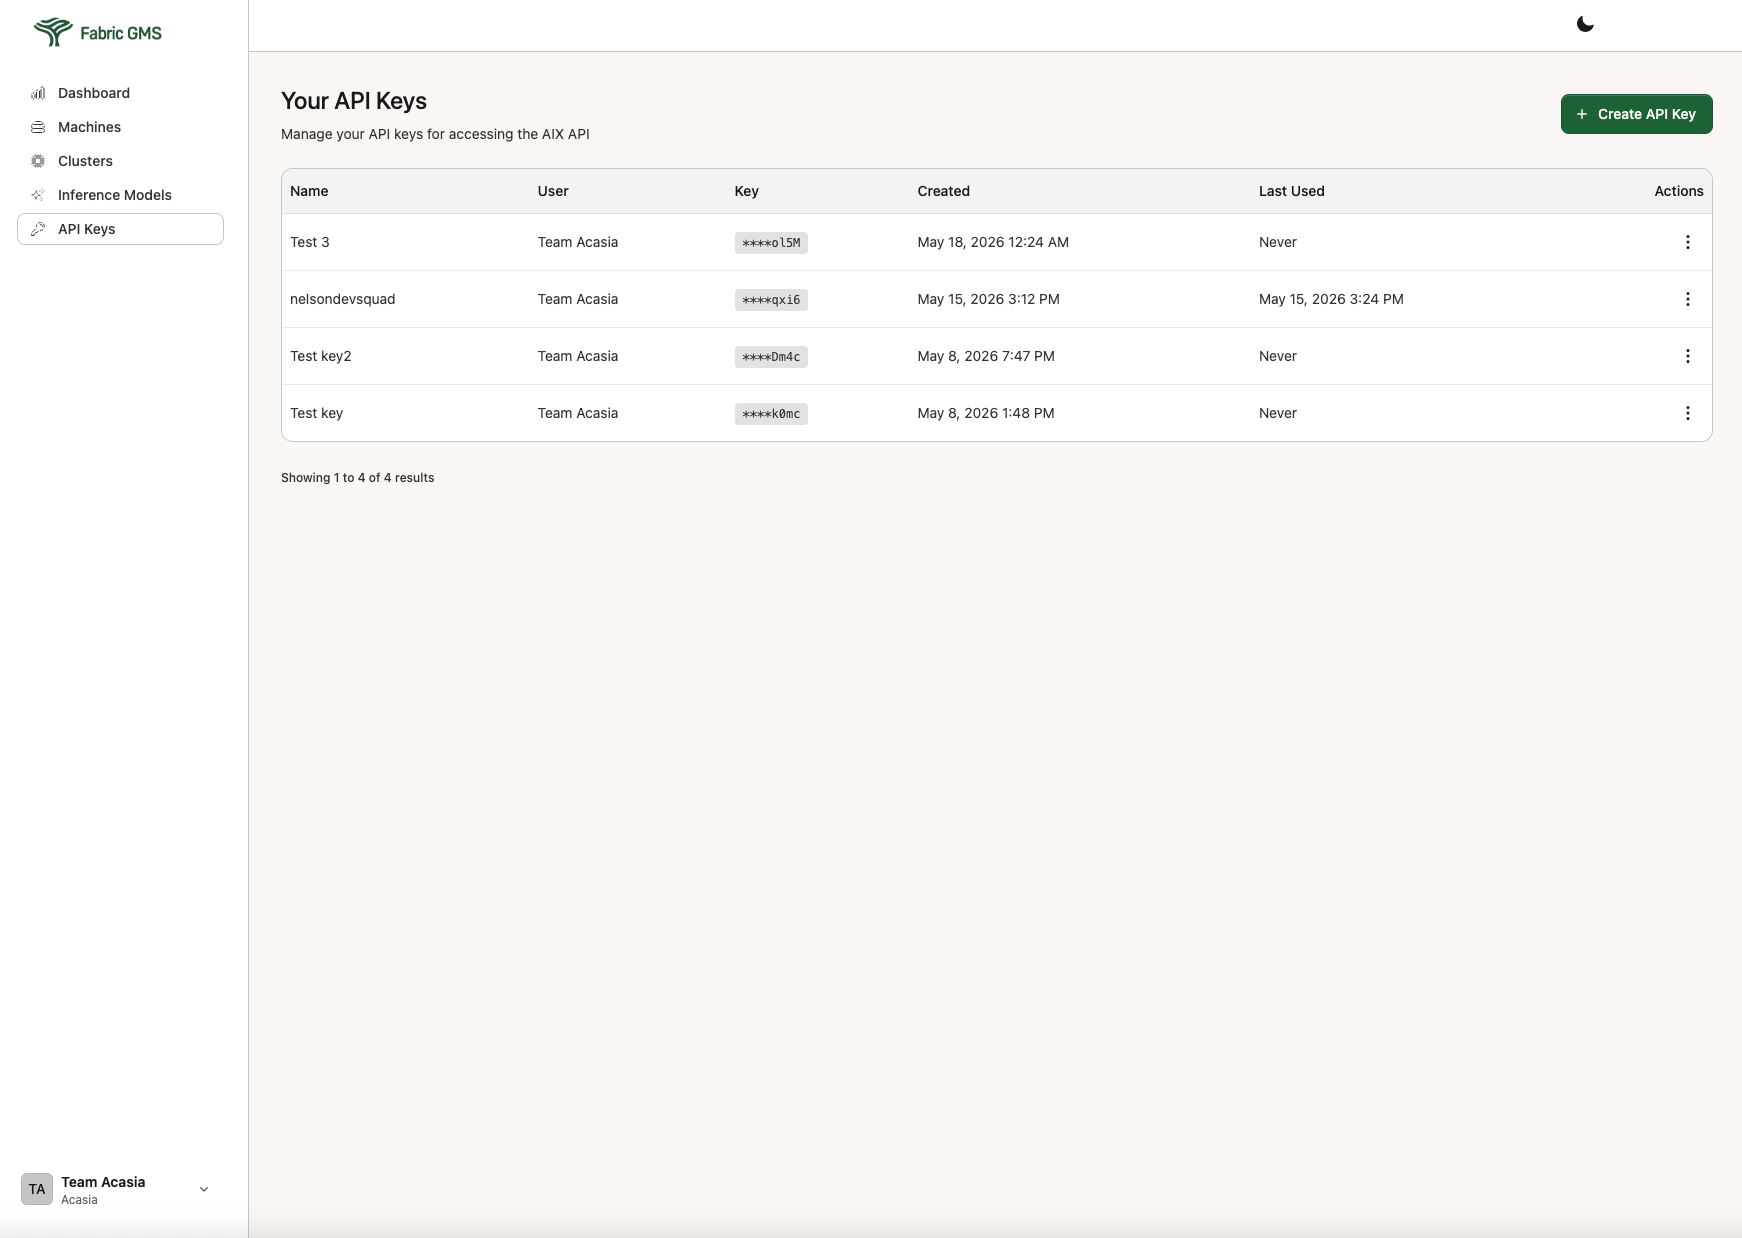
 API keys are scoped to the active organization and authenticate requests to:
- Inference endpoints
- Automated workflows and pipelines
- Acasia service integrations
API key table fields
Creating an API key
1
Click Create API Key
Opens the key creation panel.
2
Name the key
Use a name that identifies the application, environment, or owner — for example:
production-app, dev-pipeline, or team-acasia.3
Copy the key immediately
The full key value is shown only once at creation. Copy it and store it in your secrets manager before closing the panel. It cannot be retrieved again.
Using an API key
Include the API key in theAuthorization header of requests to Acasia endpoints:
Last Used timestamp
Use this column to confirm a key is actively used, identify stale keys, and audit usage across your organization.Rotating and revoking keys
Rotate a key by creating a new one, updating your application to use it, then revoking the old one. Revoke a key from the Actions menu. Revocation is immediate.Best practices
- Name keys by application, environment, or owner
- Store keys in a secrets manager
- Rotate keys periodically and whenever a team member with key access leaves
- Revoke keys immediately if exposure is suspected
- Never commit keys to source code or include them in logs
- Review the Last Used column regularly to identify and remove stale keys